
 CA
 NZ
 UK
 AU
 IND

 US

 Share
 X (Formerly Twitter)
 Whatsapp
 Facebook
 LinkedIn
 Telegram
 Email This Article
 Copy Link
 Summarize with AI
 Chat GPT
 Perplexity
Key Highlights
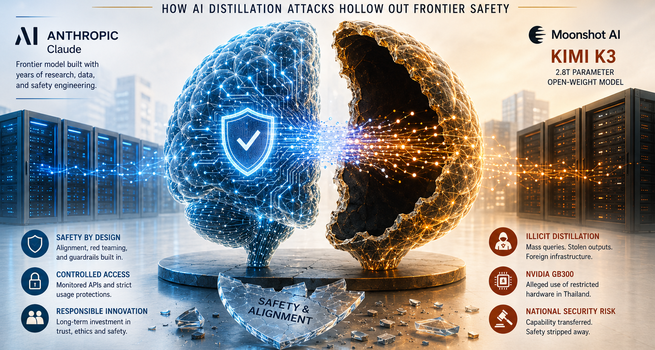
- Illicit distillation transfers frontier AI capability to rival models while stripping the safety architecture that makes that capability responsible to deploy.
- Anthropic identified campaigns by Moonshot AI, DeepSeek, and MiniMax generating over 16 million exchanges via approximately 24,000 fraudulent accounts to extract Claude's capabilities.
- US officials allege Moonshot AI distilled Anthropic's Fable model to build Kimi K3, its 2.8 trillion-parameter open-weight model, compounding risk through unrestricted public release.
- White House adviser Michael Kratsios and Treasury Secretary Scott Bessent have signalled sanctions as a policy response, marking an escalation beyond export control enforcement.
- The alleged use of restricted Nvidia GB300 hardware in Thailand links the distillation campaign to chip smuggling enforcement, converging two separate regulatory frameworks at a single target.
The Real Risk Is Not What Was Taken
The global AI industry spent the week of 17 July 2026 debating whether Kimi K3 had narrowed the gap between Chinese and American frontier models. That debate, while commercially significant, misses the more consequential question.
Moonshot AI's release of a 2.8 trillion-parameter open-weight model with a one-million-token context window and native vision capabilities is a technical milestone. But if US government allegations are accurate, the capability embedded in K3 was not built from scratch. It was systematically extracted from a proprietary American model. And in that extraction, something critical was left behind.
Frontier AI models are not just capability engines. They are layered systems in which safety architecture, developed through deliberate and resource-intensive alignment work, sits alongside the base model. Illicit distillation acquires the former while bypassing the latter entirely. What proliferates is not a copy of a frontier model. It is a frontier model with its safeguards removed.
That distinction is the story.
The Legitimate Tool Turned Weapon
Distillation is a standard and widely used technique in AI development. A larger, more capable model generates outputs that train a smaller or more efficient version of itself. Frontier laboratories apply this routinely to produce leaner commercial variants without the cost of retraining from the ground up. The method is efficient, legally unambiguous, and produces models that inherit both the capability and the safety properties of the parent system.
The illicit version works through the same technical mechanism but operates against a competitor's proprietary system. A lab generates high volumes of structured queries against a rival's API, harvests the responses at scale, and uses those outputs as training data for its own model. The capability transfers. The research investment does not. Neither does the safety architecture.
What makes the illicit version structurally distinct is not the technique but the asymmetry it exploits. A laboratory that trains its own model controls the full pipeline, including the alignment work that constrains how the model behaves in high-risk domains. A laboratory that trains on extracted outputs inherits only what is visible in those outputs. The constraints embedded in the model through separate safety training are invisible in the response layer and therefore do not transfer.
The Anatomy of an Industrial Campaign
In February 2026, Anthropic published a detailed disclosure of three simultaneous distillation campaigns it attributed with high confidence to Chinese AI laboratories. The scale and operational sophistication of what it found reframed the issue from incidental misuse to coordinated industrial activity.
Moonshot AI generated over 3.4 million exchanges with Claude through hundreds of fraudulent accounts spanning multiple access pathways. The campaign targeted agentic reasoning, tool use, coding, data analysis, computer vision, and computer-use agent development. Attribution was established through request metadata matching the public profiles of senior Moonshot staff. In a later phase, the campaign shifted toward extracting and reconstructing Claude's reasoning traces directly.
DeepSeek conducted approximately 150,000 exchanges with a more targeted focus. Prompts were structured to elicit chain-of-thought reasoning sequences, effectively generating training data for reinforcement learning at scale. A subset of the campaign produced censorship-safe alternatives to politically sensitive queries, suggesting parallel objectives beyond pure capability extraction.
MiniMax ran the largest campaign, generating over 13 million exchanges. Anthropic detected this operation while it was still active, before MiniMax had released the model under development. When Anthropic released a new model during the active campaign, MiniMax redirected nearly half its traffic to the updated system within 24 hours, indicating a responsive and professionally managed operation.
The infrastructure behind all three campaigns followed a common architecture. Proxy services operated networks of fraudulent accounts distributed across Anthropic's API and third-party cloud platforms, mixing distillation traffic with ordinary usage to complicate detection. In one documented instance, a single proxy network managed more than 20,000 fraudulent accounts simultaneously. Anthropic described these as hydra cluster architectures: networks with no single point of failure, where banned accounts are replaced automatically by new ones.
What Transfers and What Does Not
The IP framing of illicit distillation, while accurate, understates the structural risk. The more significant problem is what the process cannot replicate.
Safety architecture in frontier AI models is not a feature layer applied on top of base capability. It is the product of separate, deliberate training processes that shape how the model responds in domains with elevated risk of harm. These include refusals and mitigations around content that could assist in the development of biological or chemical weapons, constraints on facilitating offensive cyber operations, and alignment frameworks designed to prevent models from supporting malicious actors in high-consequence scenarios.
This architecture is not encoded in the model's response to any given query. It is embedded through training that is distinct from, and subsequent to, the development of base capability. A model trained on harvested outputs acquires the performance profile visible in those outputs. The underlying constraints, which are not surfaced in individual responses, do not transfer.
The result is a model that approximates frontier capability in benchmark terms while lacking the alignment infrastructure that made the original safe to deploy. Anthropic's disclosure made the downstream consequence explicit. Models built through illicit distillation without these safeguards create accessible pathways for state and non-state actors seeking frontier-level capability for applications the original system was specifically designed to refuse: offensive cyber operations, disinformation infrastructure, weapons development assistance.
The risk compounds when a distilled model is released as an open-weight system. At that point, the capability becomes freely replicable by any actor with sufficient compute, with no governance mechanism attached and no safety obligation on downstream users.
Kimi K3 and the Open-Weight Complication
Kimi K3 crystallises both the competitive and the safety dimensions of this problem in a single event.
Moonshot positioned the model as a contribution to the global open-source community. The full model weights were scheduled for public release on 27 July 2026, making K3 the first model of its parameter scale to be freely downloadable and customisable. Moonshot acknowledged that K3 trailed the most capable US proprietary models in overall performance but claimed competitive results across its evaluation suite and noted improvements in scaling efficiency relative to its predecessor.
On 22 July 2026, White House science and technology adviser Michael Kratsios stated publicly that the US government had information that Moonshot distilled Anthropic's Fable model during K3's development. Kratsios added a second allegation: Moonshot had acquired servers equipped with Nvidia's GB300 Grace Blackwell chips and had accessed that infrastructure in Thailand, likely to conduct model training in circumvention of US export controls on advanced semiconductors introduced in 2022.
The chip allegation matters beyond its evidentiary role in the distillation case. It connects two enforcement frameworks that have until now operated in parallel. Export controls on advanced Nvidia hardware were designed to limit China's ability to train frontier models by restricting access to the compute required. If Moonshot conducted large-scale distillation using restricted hardware accessed through a third country, both the capability extraction and the infrastructure used to process it fall within the scope of existing US regulatory concerns. The two threads converge at the same development pipeline.
Treasury Secretary Scott Bessent drew the policy line directly. Open-source AI development and industrial-scale distillation of American proprietary models are not equivalent activities. The former advances a public good. The latter is intellectual property theft with national security consequences.
Policy Escalation and Market Consequences
The arc from Anthropic's February disclosure to the July government response reflects a deliberate shift in how the US is treating distillation attacks: from an industry-level enforcement matter to an executive branch priority with sanctions as a stated instrument.
Anthropic's February publication detailed the technical indicators of each campaign and called for coordinated response across the AI industry, cloud providers, and policymakers. The company had already strengthened verification requirements for the account categories most frequently exploited to establish fraudulent access and was sharing technical indicators with other laboratories and relevant authorities.
By April 2026, a White House memo from Kratsios characterised these campaigns as systematic efforts to undermine American research and development. The July escalation, with Bessent explicitly naming sanctions as a consequence for companies that cross into industrial IP theft, marks a further step: a declared policy instrument rather than a framing document.
For investors assessing US AI companies, the distillation issue raises durable questions about the structure of competitive advantage. If frontier capability can be extracted and replicated at a fraction of original development cost, the return on research and development investment is structurally compressed. The degree to which safety architecture constitutes an independently defensible moat, and the extent to which regulation enforces that distinction, will increasingly shape valuation frameworks for AI companies over the medium term.
The open-weight release of K3 also tests a market assumption that has held broadly until now: that open-source AI and proprietary AI represent distinct competitive categories. A model trained in part on extracted frontier capability and released without restriction potentially reduces the marginal value of every proprietary model it approximates, while bearing none of the development cost or safety obligation.
The window for establishing enforceable norms around distillation is narrow. The technical capacity to conduct campaigns at this scale is not diminishing. Whether the current combination of corporate disclosure, industry coordination, export controls, and sanctions threats constitutes a sufficient deterrent is a question that the trajectory of Chinese AI development over the next 12 to 18 months will answer empirically.
This article is for informational and analytical purposes only and does not constitute financial or investment advice. It does not represent a recommendation to buy, sell, or hold any security. Kalkine Media makes no representation as to the accuracy or completeness of the information contained herein. Readers should conduct their own due diligence before making any investment decisions.

 Nov 04, 2026
 Please wait processing your request...